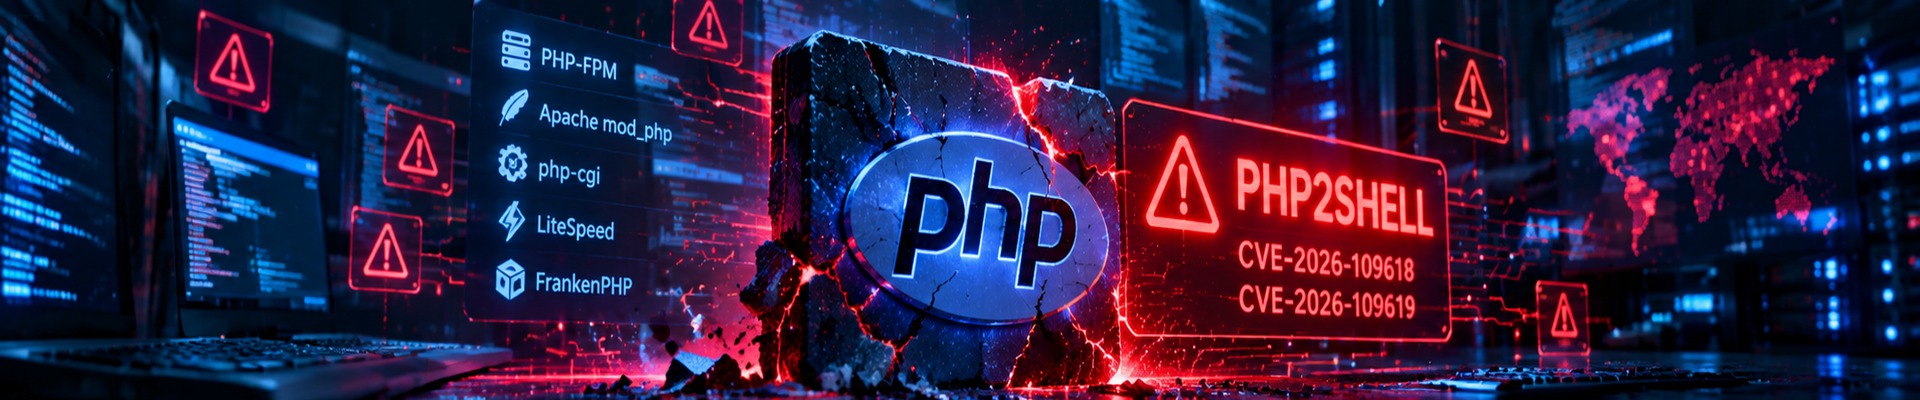
PHP2Shell: The Critical PHP Exploit That Sent the Internet Into Emergency Mode
Posted on: October 24, 2026
by: Nadim Younes, Founder | Business Strategist
Two critical vulnerabilities in the PHP engine triggered emergency security updates worldwide. The PHP2Shell incident is a powerful reminder that even the technology running beneath millions of websites can become a serious security risk.
When the Foundation of the Web Becomes Vulnerable
On October 21, 2026, the PHP development team released emergency security updates addressing two critical vulnerabilities capable of allowing unauthenticated remote code execution.
The vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, became widely known as PHP2Shell.
Both received a critical CVSS 4.0 severity score of 9.2 out of 10.
The announcement prompted urgent action from hosting providers, server administrators, software developers, and cybersecurity teams worldwide.
Some organizations temporarily took websites offline while evaluating their exposure and implementing security updates.
But what made this incident particularly serious was not simply the number of potentially affected websites.
The vulnerabilities existed within PHP itself, the programming engine powering a substantial portion of the modern web.
Unlike an ordinary application vulnerability, this incident demonstrated how a weakness in a foundational technology could expose numerous otherwise unrelated applications.
What Exactly Is PHP2Shell?
PHP2Shell refers to two critical security vulnerabilities affecting the PHP runtime.
PHP is a server-side programming language used by countless websites and web applications, including WordPress, Drupal, Laravel applications, e-commerce platforms, and custom business systems.
Under vulnerable conditions, PHP2Shell could allow an attacker to execute unauthorized code on a server without first authenticating.
This is known as unauthenticated remote code execution, or RCE.
Depending on the affected configuration and the privileges of the PHP process, successful exploitation could potentially allow attackers to:
- Execute malicious commands within the compromised environment.
- Access sensitive application files and configuration data.
- Attempt to obtain database credentials or authentication tokens.
- Modify website content or deploy additional malicious software.
- Establish unauthorized access to affected systems.
Researchers also demonstrated memory-disclosure techniques that could expose sensitive information handled by PHP processes.
The actual impact depends on the affected environment, its configuration, and the permissions available to the compromised process.
Why This Was Different From a Typical Website Vulnerability
Most website owners are familiar with security warnings involving outdated WordPress plugins, vulnerable themes, or insecure application code.
PHP2Shell presented a different category of risk.
The vulnerabilities affected the underlying PHP runtime rather than a particular content management system.
This meant that updating WordPress, changing a theme, or removing a suspicious plugin would not, by itself, resolve the underlying PHP vulnerabilities.
The official PHP advisory identified multiple web-serving environments as potentially affected, including PHP-FPM, Apache mod_php, php-cgi, LiteSpeed, and FrankenPHP.
The PHP team highlighted Apache mod_php as a particularly high-risk configuration because researchers demonstrated an attack that could be triggered before application code executed.
In practical terms, even a carefully maintained website could remain exposed if its underlying PHP runtime had not received the necessary security fixes.
A secure application still depends on the security of the infrastructure executing it.
The Emergency Response: PHP Releases Critical Updates
On October 21, the PHP development team released patched versions addressing both vulnerabilities.
The emergency security releases included:
| PHP Branch | Security Release |
|---|---|
| PHP 8.5 | 8.5.12 |
| PHP 8.4 | 8.4.27 |
| PHP 8.3 | 8.3.36 |
| PHP 8.2 | 8.2.35 |
Administrators were urged to update immediately.
For systems using distribution-maintained or extended-support PHP packages, administrators must verify that the relevant security fixes have been incorporated into their installed packages, including through vendor backports where applicable.
A version number alone does not always establish whether a vendor-maintained package is protected.
Older unsupported PHP installations require particular attention because they may not receive official upstream security updates.
The PHP development team also emphasized that there were no complete mitigations for these vulnerabilities.
Installing verified security fixes remains the essential protective action.
Cloudflare and the Wider Security Industry Respond
The incident also prompted action from major cybersecurity and infrastructure providers.
Cloudflare announced protective measures designed to detect and block exploitation attempts targeting PHP2Shell.
Security researchers and infrastructure vendors published technical guidance, indicators of potential exploitation, and recommendations for assessing affected systems.
However, web application firewalls and network-edge protections should be understood as additional security layers rather than replacements for software updates.
A firewall may reduce exposure to known attack patterns, but it cannot guarantee protection against every exploitation technique.
This distinction is particularly important when vulnerabilities exist inside the programming runtime itself.
The most effective response combines verified software updates, layered defenses, monitoring, and appropriate incident-response procedures.
What Website Owners and Businesses Should Do
The PHP2Shell incident offers several practical lessons for businesses relying on PHP-based websites and applications.
1. Verify Your PHP Security Status
Ask your hosting provider or technical administrator whether the PHP runtime serving your website has received the relevant security fixes.
For vendor-maintained PHP packages, request confirmation of the applicable security advisory or backported patch.
2. Keep Applications and Dependencies Updated
Although application updates do not directly fix PHP2Shell, maintaining WordPress, Laravel applications, plugins, and third-party dependencies remains essential for reducing other security risks.
3. Use Layered Infrastructure Protection
Server hardening, application isolation, malware detection, network-edge protections, and properly configured access controls can help reduce exposure and limit the consequences of a compromise.
No single technology provides complete protection.
4. Maintain Recoverable Backups
Regular backups should be protected and periodically tested.
If a server or application is compromised, recovery may require more than restoring files. Credentials, application integrity, and the security of the restored environment must also be assessed.
5. Understand Your Hosting Provider’s Responsibilities
Website owners should know who is responsible for maintaining PHP runtimes, installing server security updates, monitoring infrastructure, and responding to critical vulnerabilities.
These responsibilities should be clear before an emergency occurs.
Host2Media: Security Requires More Than a Hosting Account
At Host2Media, we believe that professional web hosting requires continuous attention to the infrastructure supporting every website and application.
The PHP2Shell incident demonstrates why server administration, software lifecycle management, and security awareness are essential components of a reliable hosting service.
Our managed hosting environments incorporate multiple security and infrastructure technologies, including:
CloudLinux
Resource management and hosting-account isolation capabilities designed to support stable shared hosting environments.
CageFS
Account-level filesystem isolation that helps separate hosted environments and reduce unnecessary cross-account access.
Imunify360
Server security capabilities incorporating malware detection, protective controls, and threat monitoring.
Cloudflare
Network-edge security capabilities that can help filter malicious traffic and provide additional protection against common web-based attacks.
Professional Infrastructure Administration
Ongoing server maintenance, operational oversight, and evaluation of security developments affecting web hosting technologies.
These measures contribute to a layered infrastructure security approach.
However, it is important to recognize that technologies such as account isolation, malware scanning, and web application firewalls do not replace the need to patch vulnerable PHP runtimes.
At Host2Media, we follow security developments affecting the hosting industry and evaluate their relevance to the environments we manage.
Our philosophy is straightforward:
Security is not a feature installed once. It is an ongoing operational responsibility.
A New Reality for the Web Hosting Industry
PHP2Shell illustrates how quickly a vulnerability in a widely deployed technology can become an industry-wide emergency.
A critical security issue does not necessarily begin with a compromised website, a stolen password, or an outdated plugin.
Sometimes, the weakness exists several layers beneath the application itself.
For businesses, this reinforces the importance of choosing hosting services based on more than storage space, bandwidth, or price.
Infrastructure maintenance, technical expertise, security updates, and clearly defined operational responsibilities matter.
No hosting environment is immune to every vulnerability.
But organizations that understand their infrastructure, maintain supported technologies, and respond systematically to security advisories are better positioned to manage emerging threats.
The next critical vulnerability may be impossible to predict. Preparing for it should not be.
Host2Media | Managed Web Hosting & Infrastructure Security
Your business depends on more than a functioning website.
It depends on the infrastructure, software, and security practices supporting that website every day.
At Host2Media, we provide professionally managed web hosting solutions focused on infrastructure reliability, security, and ongoing technical administration.
From corporate websites and e-commerce platforms to custom web applications, we understand the importance of maintaining the technology behind your digital presence.
Host2Media. Hosting backed by technical expertise.
-

share
-

-

-

More similar topics
When the Cloud Goes Down, Does Your Business Go Down With It? Your AI Application Could Be Compromised Before It Even Starts Stop Roasting Your Laptop: Why Closing the Lid Doesn’t Turn It Off (And Other PC Sins) Honoring Labor Day: A Salute to Every Worker The Anatomy of a Secure Website: Essential Features Every Business NeedsCopyright © 2024, Host2Media,